
No downloads
Runs everywhere
- Windows
- Mac
- Linux
- Docker
Without downloading any binary!
Quickest way to


The Web Debugger is now built into the Pinggy Dashboard. Inspect, modify, and replay your tunnel traffic right in the browser.


01Live request log, with bandwidth and request counters

02Request and response headers of a single request
Your machine opens one outbound, encrypted connection to Pinggy, and clients reach it through a public address. No port forwarding, no firewall changes. Pick a tunnel type to see how the traffic flows.
Visitors get an https:// URL. Pinggy terminates TLS with a certificate it issues for that URL, then sends each request down the encrypted SSH tunnel to localhost:8080.
Clients connect to a public TCP port. Pinggy forwards the bytes as they are through the encrypted SSH tunnel, so protocols with their own encryption, like SSH or a database over TLS, stay encrypted end to end.
Pinggy reads only the hostname (SNI) to route the connection and never decrypts it. Your server holds the certificate, so traffic stays encrypted from the client all the way to localhost:443.
Datagrams sent to a public UDP port travel through the encrypted tunnel opened by the Pinggy CLI to localhost:19132. UDP tunnels need the CLI, since plain SSH only carries TCP.
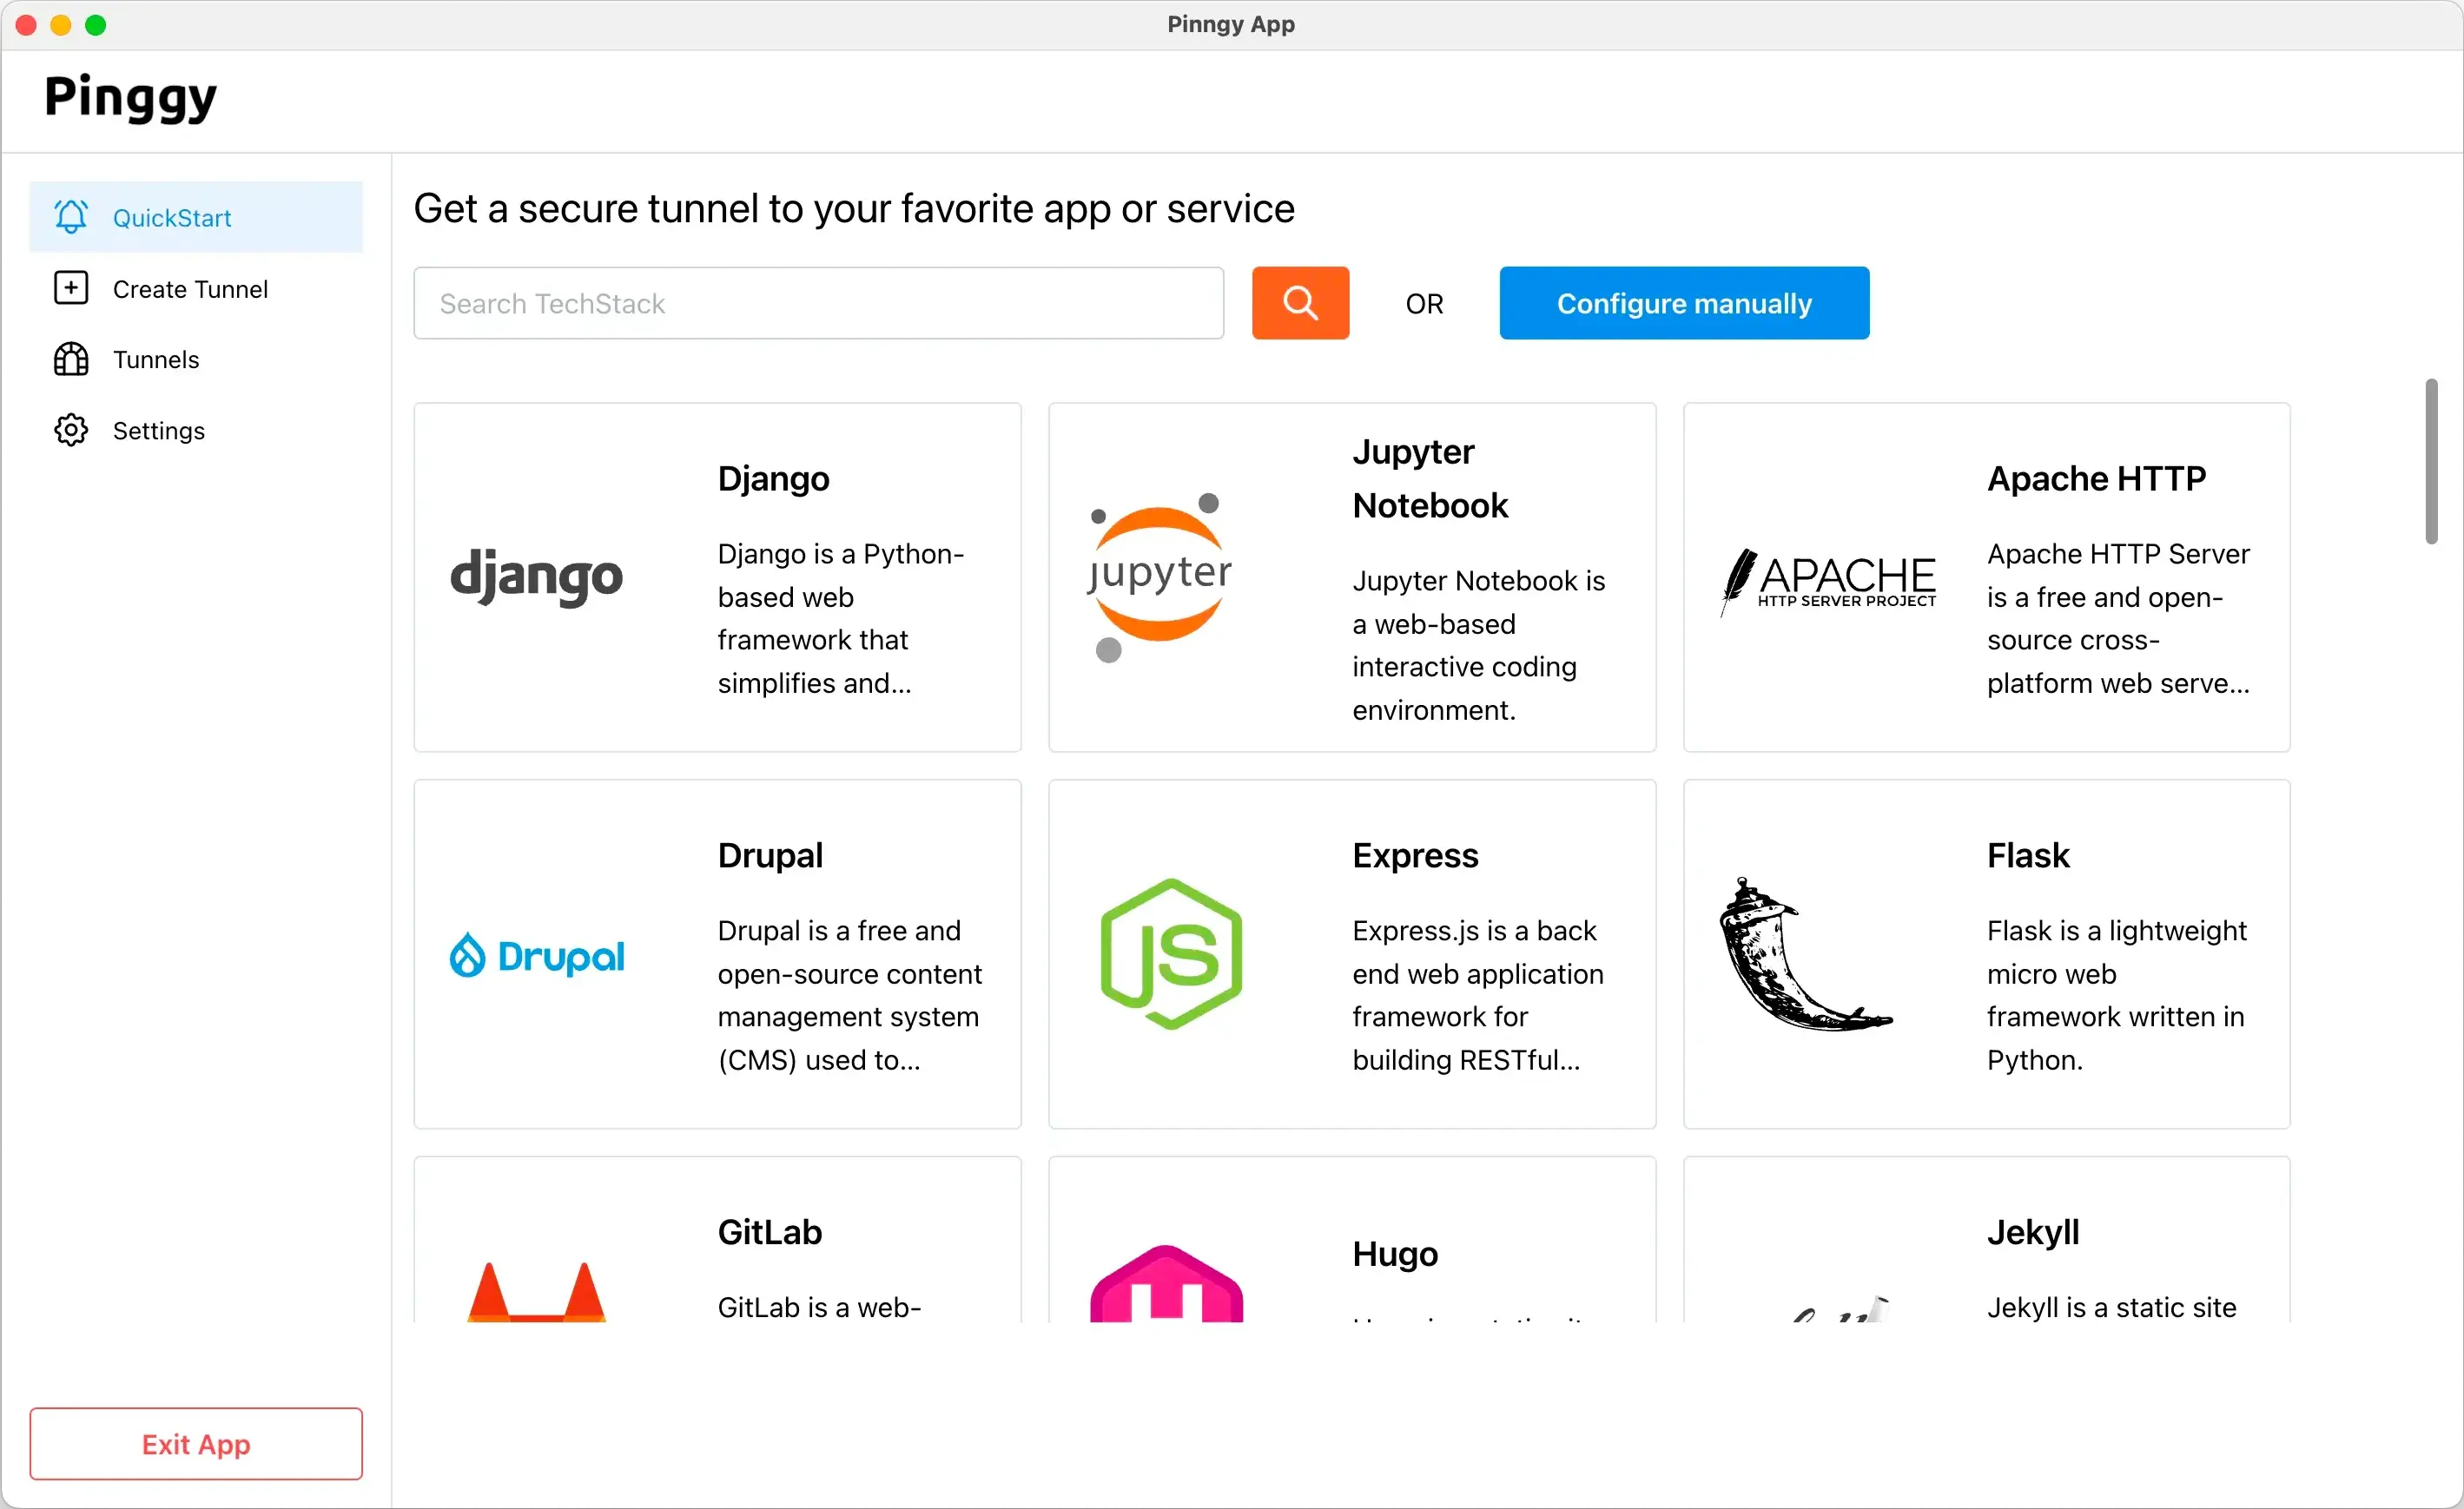
Runs everywhere
*.yourdomain.com routes different subdomains to different ports.Fast tunnels worldwide
Make your development experience smoother by unlocking the full potential of Pinggy.
0/month
Free for life
/month
billed annually · seats
/month
billed monthly · seats



If the ssh command prompts you for a password you can just press enter (a blank password). Or you can type in something random and press enter.
ssh-keygenIn windows, sometimes, the ssh tunnel cannot reach localhost
because of some bug in the ssh client.
Replace localhost with
127.0.0.1 in your Pinggy command.
Example:
Pinggy relies on SSH remote port forwarding. The option
-R 0:localhost:8000 in the command only implies
that connections to the public URL given by pinggy are
forwarded to your localhost:8000.
No other port than the one specified by you can be accessed by Pinggy or by anyone through the public URLs provided by Pinggy.
You can read more about the -R option of openssh
client
here. If you are using a different ssh client, then refer to its
documentation.
free.pinggy.io is routed to the Pinggy server
nearest to your location. Currently we have our servers in
USA, Europe, UK, Singapore, Brazil, and Australia.
Pinggy's free plan has a tunnel timeout of 60 minutes. If the tunnel is closed by you or reaches the time limit, starting a new tunnel will generate a new URL.
To obtain a permanent or persistent URL, or to use your own domain, you must subscribe to Pinggy Pro.
Yes. Current versions of Windows, Mac, as well as almost all Linux distributions come with openssh client pre-installed. Therefore Pinggy will just work out of the box.
To learn more about using Pinggy on Android read our blog post.
You can use TCP and TLS tunnels for free with Pinggy. Click on "Advanced Settings" on the top of the homepage, and select TCP.
Read our guide on long running tunnels here.
Pinggy automatically renews certificates if it finds the opportunity when the tunnel is not active. However, still if certificate has expired, it can be renewed manually from https://dashboard.pinggy.io/domains . Click on the edit icon on the domain, and click Custom Domain tab.
Make sure you do not add any arbitrary argument after the SSH command.
One common reason for this is that an existing tunnel with the same token is active.
Terminate your existing tunnel with the same token. You can do so from the Active Tunnels option in the dashboard.
You can also use the Force option in the dashbaord.
Pinggy does read tunnel traffic for providing the Web Debugger feature.
Use TLS tunnels for Zero trust mode, where Pinggy cannot read your data. In this case your traffic is end-to-end encrypted.