In this article

Every time a device on your network looks up a hostname, that query goes to whatever DNS server you’ve configured - and for most people, that is still a resolver run by their ISP, Google (8.8.8.8), or Cloudflare (1.1.1.1). Self-hosting your own DNS server hands that control back to you: no third party sees your lookup history, you can block ads and trackers before they ever reach a device, and you get to decide exactly how internal hostnames, split-horizon zones, and DNSSEC are handled on your network.
The open source DNS ecosystem splits into two fairly different categories, and mixing them up is the most common mistake people make when picking a server. The first category is authoritative nameservers and infrastructure-grade software - PowerDNS, BIND, NSD, Knot DNS, and CoreDNS - built to host zones, sign them with DNSSEC, and handle high query volumes. The second is home and small-office resolvers and forwarders - Unbound, Pi-hole, AdGuard Home, Blocky, and SmartDNS - most of which forward to an upstream resolver, cache answers, and block ad/tracker domains; Unbound is the exception that resolves recursively on its own. Technitium DNS Server straddles both.
If you run any of these in 2026, the thing to plan for is security. Between August and October, BIND fixed 18 CVEs across two releases, Unbound fixed 14, NSD fixed 8, and Pi-hole patched two high-severity remote code execution bugs in its FTL engine. Whichever server you pick, plan to patch it monthly. Versions, star counts and licenses below were checked on October 27, 2026.
Summary
Infrastructure-grade (authoritative/recursive): CoreDNS, Technitium DNS Server, PowerDNS, BIND 9, NSD, Knot DNS - full DNS servers for hosting zones or resolving recursively.
Home/lab-grade (resolvers, forwarders & ad-blocking): Unbound, Pi-hole, AdGuard Home, SmartDNS, Blocky, dnsmasq - most sit in front of an upstream resolver and block ads/trackers, though Unbound resolves recursively on its own.
Patch on a schedule: BIND, Unbound, NSD, PowerDNS, Knot DNS, Pi-hole and Technitium all shipped security releases between August and October 2026. ISC now expects security fixes in every monthly BIND release and has pushed BIND 9.22 to the end of 2026 at the earliest.
Quick test any of them: dig @<server-ip> -p <port> example.com +short
Why Self-Host Your Own DNS Server
The most immediate reason is privacy. Every domain you resolve tells your DNS provider what site you’re about to visit, and that log persists somewhere outside your control unless you run the resolver yourself. The second reason is blocking - a DNS server that refuses to resolve known ad and tracker domains protects every device on your network (phones, smart TVs, IoT gadgets) without installing an extension anywhere, something browser-based ad blockers can’t do. The third reason is control: split-horizon DNS for a homelab or VPN, custom internal TLDs, Response Policy Zones for threat intel, or just not being at the mercy of a public resolver’s outage. And if you run any kind of internet-facing service, an authoritative server you manage yourself is how you actually own your zone data instead of trusting a registrar’s default nameservers. For the fundamentals of how any of this resolution actually works, see our explainer on what problems DNS solves.
Comparison Table: Authoritative & Recursive DNS Servers
| Server | GitHub Stars | License | Language | Latest (Oct 2026) | Mode |
|---|---|---|---|---|---|
| CoreDNS | 14.4K+ | Apache-2.0 | Go | 1.15.0 | Authoritative + forwarder (plugin-dependent) |
| Technitium DNS Server | 10.2K+ | GPL-3.0 | C# | 15.6.2 | Authoritative + Recursive + DHCP |
| PowerDNS | 4.5K+ | GPL-2.0 | C++ | Auth 5.1.5, Recursor 5.4.9 | Authoritative + Recursive |
| BIND 9 | 785+ | MPL-2.0 | C | 9.20.30 | Authoritative + Recursive |
| NSD | 574+ | BSD-3-Clause | C | 4.15.4 | Authoritative only |
| Knot DNS | 329+ | GPL-2.0-or-later | C | 3.6.2 | Authoritative only |
Comparison Table: DNS Forwarders, Caches & Resolvers
| Server | GitHub Stars | License | Language | Latest (Oct 2026) | Mode |
|---|---|---|---|---|---|
| Pi-hole | 61.5K+ (core) / 1.7K+ (FTL) | EUPL-1.2 | Shell (core) / C (FTL) | Core 6.5, FTL 6.8, Web 6.6.1 | Forwarder + blocking + DHCP |
| AdGuard Home | 37.7K+ | GPL-3.0 | Go (TypeScript UI) | 0.107.79 (beta 1.0.0-b.1) | Forwarder + blocking + DHCP |
| SmartDNS | 11.3K+ | GPL-3.0 | C | Release 48.4 | Forwarder (fastest-IP racing) |
| Blocky | 7K+ | Apache-2.0 | Go | 0.35.0 | Forwarder + blocking |
| Unbound | 5K+ | BSD-3-Clause | C | 1.26.2 | Recursive (validating) |
Why DNS Servers Ship So Many Security Fixes in 2026
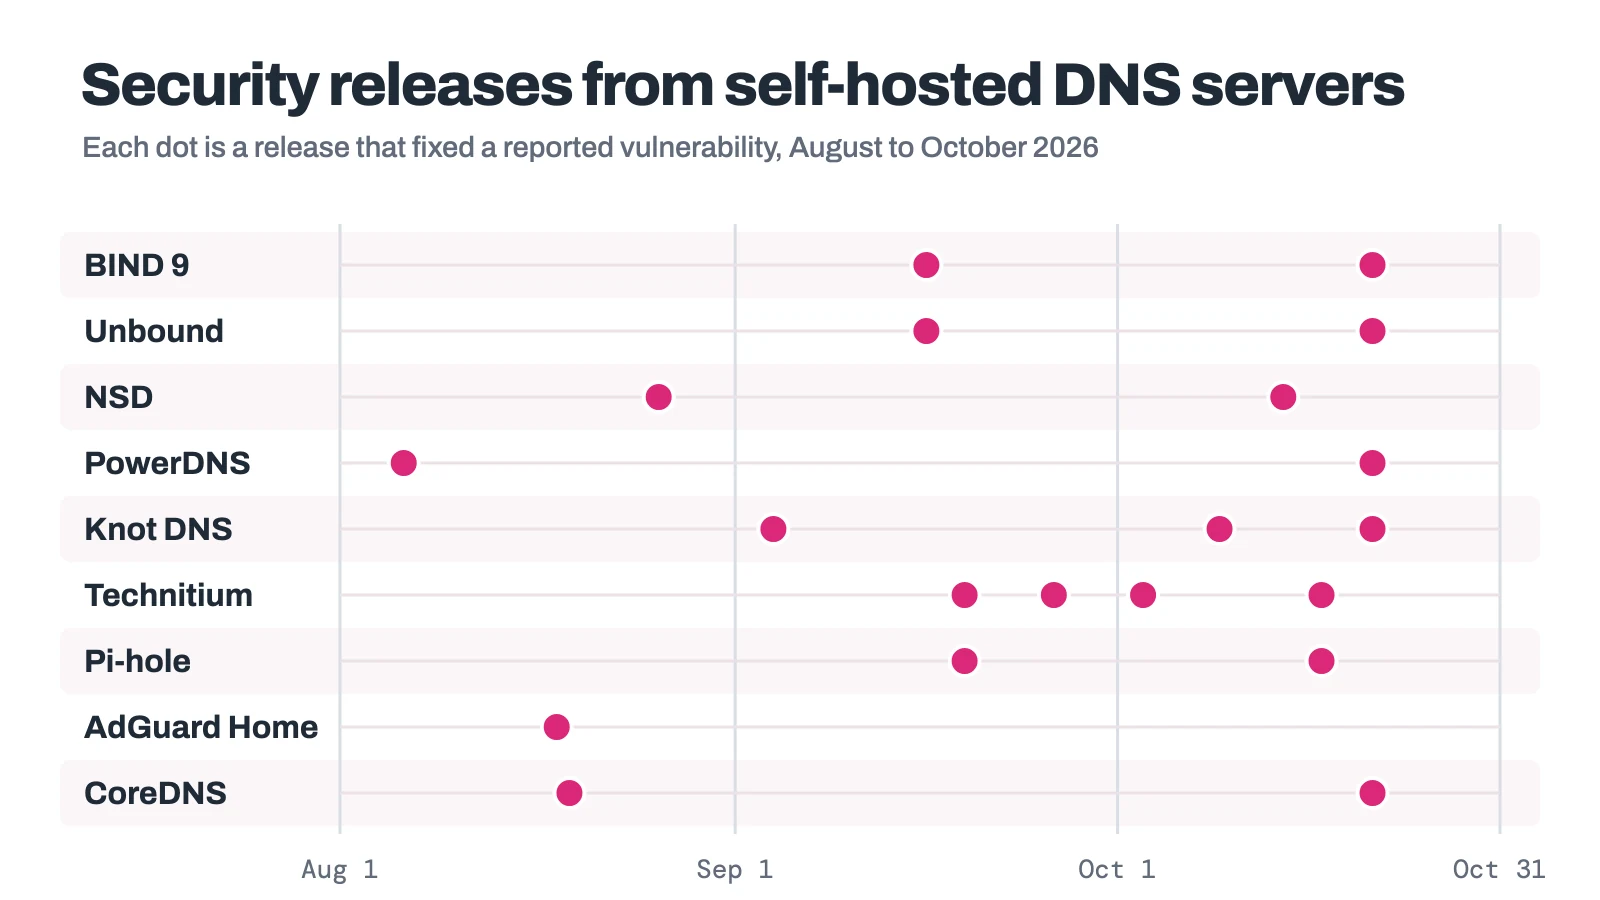
Data: release notes and security advisories from ISC, NLnet Labs, PowerDNS, CZ.NIC, Technitium, Pi-hole, AdGuard and CoreDNS, checked October 27, 2026.
The pace of security releases in this space has picked up sharply, and ISC has said why. In a May 2026 post, it wrote that large language models “are making it much easier to find software vulnerabilities in open source” and that it was triaging reports “at a rate that exceeds 10X the historic levels.” The credits in recent release notes tell the same story: NLnet Labs and Technitium now credit reports from Anthropic and Ada Logics, and one NSD fix thanks “Claude and Ada Logics” by name.
One day shows the pattern clearly. On October 21, BIND 9.20.30, PowerDNS (Authoritative 5.1.5 and Recursor 5.4.8), Unbound 1.26.2 and Knot DNS 3.6.2 all shipped fixes for crafted DNS name compression pointers that burn CPU during parsing. The takeaway: subscribe to your vendor’s security announcements and treat DNS server updates like browser updates, not a quarterly chore.
Authoritative & Recursive DNS Servers
These are the servers you reach for when you need real internet-facing DNS infrastructure: hosting your own zones, running a validating recursive resolver, or both.
1. CoreDNS - Kubernetes’ Default Cluster DNS

Screenshot: github.com/coredns/coredns/releases, October 2026.
CoreDNS takes a completely different architectural approach: instead of one monolithic daemon with built-in features, it’s a Caddy-style plugin chain, where each plugin does one job and you compose them into a Corefile. The kubernetes plugin turns it into cluster-wide service discovery, the forward plugin makes it a forwarder, the file/auto plugins serve authoritative zones (including pre-signed DNSSEC zones), and the dnssec plugin signs answers on the fly. There is no built-in recursive resolver; for that you compile in the external unbound plugin, which wraps libunbound. So what CoreDNS is depends entirely on which plugins you load. That flexibility, plus CNCF graduation in January 2019, is why it has been Kubernetes’ default DNS server since version 1.13, though it works fine as a standalone server too.
Its two most recent releases added a lot. v1.14.7 (August 19) brought ACME-managed TLS, topology-aware Kubernetes services, HTTP/2 forwarding and secondary zone management, and fixed two ACL bugs, including one where autopath could bypass ACL checks. v1.15.0 (October 21) lets the forward plugin use DNS-over-QUIC upstreams and adds opt-in JSON query logging, authenticated RFC 2136 dynamic updates and PROXY protocol v2 metadata. Both were also rebuilt on newer Go versions for Go’s own CVE fixes.
Key Features:
- Caddy-style plugin-chain architecture - compose exactly the features you need
autopathplugin to reduce Kubernetes DNS resolution latency- On-the-fly DNSSEC signing via the
dnssecplugin - Prometheus metrics via the
prometheusplugin (defaultlocalhost:9153)
License: Apache-2.0 | Language: Go | GitHub Stars: 14.4K+ | GitHub
2. Technitium DNS Server - The Most Feature-Complete Self-Hosted Option

Screenshot: technitium.com/dns, October 2026.
Technitium DNS Server is the one server in this guide that genuinely straddles both categories: it’s a real recursive resolver that walks the DNS hierarchy from the root down (not just a forwarder), it can serve as an authoritative server for zones you own with primary/secondary/stub/conditional-forwarder zone types, and it ships a built-in DHCP server, all behind a full web console. For admins who want Pi-hole-style ease of use without giving up authoritative DNS or genuine recursion, this is the closest thing available.
Protocol support is comprehensive: DoT, DoH (HTTP/1.1, HTTP/2, HTTP/3), and DoQ as both a client and a server, DNSSEC validation across RSA/ECDSA/EdDSA, DANE/TLSA, and zone transfers over TLS or QUIC. Version 15.0 (April 2026) added Single Sign-On via OpenID Connect, and version 15.5 (September 19) added LDAP authentication, a zone file editor in the web console, and a Docker health check. It has also been busy on security: 15.5 alone fixed two cache poisoning bugs, a DNSSEC validation bypass through out-of-bailiwick DS records and a 4,096:1 amplification path, and 15.5.1, 15.6 and 15.6.2 (October 17) each fixed more.
Key Features:
- Genuine root-to-authoritative recursive resolution, not just forwarding
- Primary/Secondary/Stub/Conditional-Forwarder zone types with AXFR/IXFR
- HTTP API, multi-user RBAC, non-expiring API tokens, and TOTP 2FA
- SSO via OpenID Connect (v15.0) and LDAP authentication (v15.5)
License: GPL-3.0 | Language: C# (.NET) | GitHub Stars: 10.2K+ | GitHub
3. PowerDNS - Database-Backed Authoritative DNS With a REST API

Screenshot: doc.powerdns.com, October 2026.
PowerDNS actually ships three separate products from one project: the Authoritative Server for hosting zones, the PowerDNS Recursor for recursive resolution, and dnsdist, a DNS-aware load balancer and firewall. What sets the Authoritative Server apart from BIND or Knot DNS is that it stores zone data in a real database - MySQL, PostgreSQL, SQLite, or LMDB - instead of flat zone files, which makes it a natural fit if you’re already managing domains through a web app or provisioning system. A built-in HTTP/JSON REST API lets you manage zones and records without touching a config file, and Lua hooks in both servers let you customize query handling. Since 5.1, Lua records are immutable by default.
The Recursor can use DoT toward forwarders and authoritative servers, sends DNS cookies (RFC 7873) against spoofing, and has generated OpenTelemetry traces since 5.3. It doesn’t serve DoT, DoH or DoQ to clients itself; that’s dnsdist’s job in front of it. Plan for regular patching: Security Advisory 2026-11 (August 6) hit the Authoritative Server, Recursor and dnsdist at once, and Advisory 2026-12 (October 21) fixed seven Recursor CVEs, including one where out-of-band NS resolution could skip DNSSEC validation and open the door to cache poisoning. Current versions are Authoritative 5.1.5, Recursor 5.4.9 (5.5 is in alpha), and dnsdist 2.1.3.
Key Features:
- Pluggable backends: MySQL, PostgreSQL, SQLite, LMDB, or BIND-style zone files
- Outgoing DoT and DNS cookies on the Recursor; DoT, DoH and DoQ for clients via dnsdist
- Online DNSSEC signing, with key rollovers handled through
pdnsutil - dnsdist for DNS-aware load balancing, rate limiting, and firewalling in front of either component
License: GPL-2.0 | Language: C++ | GitHub Stars: 4.5K+ | GitHub
4. BIND 9 - The Original Full-Featured DNS Server

Screenshot: isc.org/bind, October 2026.
BIND 9 from the Internet Systems Consortium (ISC) descends from the Berkeley Internet Name Domain package, written at UC Berkeley in the early 1980s, and ISC describes it as “the first, oldest, and most commonly deployed” DNS solution. The named daemon handles both authoritative and recursive roles in a single binary, with a feature set built up over decades: DNSSEC signing and validation, DoT and DoH (since BIND 9.18), zone transfers over TLS (XoT), Response Policy Zones for policy-based filtering, catalog zones for managing many zones as a group, and GSS-TSIG for secure dynamic updates in Windows/Active Directory environments.
2026 is the year security fixes became routine in BIND’s monthly releases. Version 9.20.29 (September 16) fixed 14 CVEs, mostly resolver crashes, resource exhaustion and DNSSEC validation bypasses, and 9.20.30 (October 21) fixed four more; 9.20.28 was withdrawn after a regression turned up in pre-release testing. Six months ago ISC was still supporting two branches, 9.18 and 9.20, but 9.18 reached end of life in June 2026, so 9.20 is now the only stable line, and ISC has deferred BIND 9.22 “until at least the end of 2026”. ISC says it will review the situation in Q4, aiming to “return to our normal release cadence in Q1 2027.” Until then, budget for a monthly patch window. Development happens on ISC’s own GitLab; the GitHub repository is a read-only mirror.
Key Features:
- DNSSEC signing and validation, with a dedicated key-signing-request (KSR) utility
- Response Policy Zones (RPZ) for reputation/threat-intel-based filtering
- Catalog zones for managing large numbers of zones as a single unit
- GSS-TSIG for secure dynamic DNS updates in Active Directory environments
License: MPL-2.0 | Language: C | GitHub Stars: 785+ (mirror) | GitHub
5. NSD - Authoritative-Only, Built for Root and TLD Operators

Screenshot: nlnetlabs.nl/projects/nsd, October 2026.
NSD (Name Server Daemon), also from NLnet Labs, takes the opposite approach from Unbound: it is authoritative-only by design, with no recursive resolution code at all. That narrow focus is deliberate - fewer code paths means a smaller attack surface and predictable, very high query throughput - and NLnet Labs says three DNS root servers and many top-level domain registries use NSD. It’s often paired with Unbound: one box for authoritative zones, another for recursive lookups.
NSD supports AXFR/IXFR zone transfers with DoT, catalog zones, and nsd-control for remote management. It shipped two security releases between August and October: 4.15.1 (August 26) fixed four CVEs, including an IP access-control bypass and two remote denial-of-service bugs, and 4.15.3 (October 14) fixed four bugs in its zone file parser that only trigger on crafted zone files, which matters if a multi-tenant provisioning system lets third parties supply zone data. Feature release 4.15.2 (September 2) added EDNS0 padding over TLS and an allow-proxy access list for the PROXYv2 port, and 4.15.4 (October 21) added a report-channel option for DNS error reporting plus more bug fixes.
Key Features:
- Multi-process query serving (
server-count) for very high queries-per-second - Catalog zone support for managing many zones as a group
- Prometheus metrics export with per-zone labels
nsd-controlfor remote, scriptable server management
License: BSD-3-Clause | Language: C | GitHub Stars: 574+ | GitHub
6. Knot DNS - High-Performance Authoritative DNS With AF_XDP

Screenshot: knot-dns.cz, October 2026.
Knot DNS is built by CZ.NIC, the registry that runs the .cz ccTLD, and like NSD it is authoritative-only (CZ.NIC ships a separate product, Knot Resolver, for recursive lookups). What makes Knot DNS distinctive is its AF_XDP mode: it uses Linux’s eXpress Data Path to process UDP, TCP and QUIC DNS traffic close to the network interface, skipping most of the kernel’s network stack for much higher packet throughput.
Knot DNS 3.6.0 (September 8) opened a new feature line. It adds early support for DELEG, the new delegation record type the IETF is working on, a “trash bin” that lets you recover deleted DNSSEC keys, and DNSSEC answer validation in kdig with +validate. It also removes TCP Fast Open support and drops packages for Debian 11 and Ubuntu 20.04. 3.6.1 and 3.6.2 (October 21) followed with hardening, including fixes for DoT 0-RTT memory exhaustion and compression-pointer abuse, and 3.5.8 fixed a TSIG bug that could let an attacker forge dynamic DNS updates. Development happens on CZ.NIC’s GitLab; GitHub hosts a mirror.
Key Features:
- Automatic DNSSEC signing with automatic or manual key rollover
- Catalog zone generation and interpretation
- Response-rate limiting to reduce abuse of authoritative answers
- TSIG-authenticated dynamic updates (DDNS)
License: GPL-2.0-or-later | Language: C | GitHub Stars: 329+ (mirror) | GitHub
DNS Forwarders, Caches & Resolvers
Most of the servers in this section sit between your devices and an upstream resolver (often 1.1.1.1, 8.8.8.8, or Quad9), cache answers, and block ad and tracker domains before they ever resolve - the home-lab-friendly counterpart to the infrastructure servers above. Unbound, grouped here for its similar home-network footprint, is the exception: it performs real recursive resolution rather than forwarding, and has no blocklist manager, though local-zone rules and RPZ can block domains.
7. AdGuard Home - The Most Polished Web UI for Network-Wide Blocking

Screenshot: adguard.com, October 2026.
AdGuard Home is a DNS forwarder and cache with network-wide ad, tracker, and phishing/malware blocking built in, plus an optional DHCP server. It ships as a single static Go binary that runs on more than 20 platform/architecture combinations, configured through a flat YAML file and a polished built-in web dashboard - which is the main reason people choose it over Pi-hole once they’ve outgrown the basics. It supports DoH, DoT, DoQ, and DNSCrypt as an upstream client, and can serve encrypted DNS itself for clients that support it.
AdGuard Home explicitly collects no usage statistics, which matters if privacy is the whole point of self-hosting DNS in the first place. The stable channel is at v0.107.79 (August 18), which hardened DNS-over-QUIC against resource exhaustion. The bigger news is on the beta channel: on September 30 it moved to a new web UI and a new version line, starting with v1.0.0-b.1. That beta drops macOS 13 Ventura support. If you expose the encrypted-DNS endpoints publicly, keep it on auto-update.
Key Features:
- Network-wide blocking with parental controls and phishing/malware filtering
- Polished built-in web UI with per-client configuration and a REST API
- Built-in DHCP server
- Single static binary across 20+ platform/architecture combinations
License: GPL-3.0 | Language: Go, with a TypeScript web UI | GitHub Stars: 37.7K+ | GitHub
8. Pi-hole - The Default Answer for Home Ad Blocking

Screenshot: pi-hole.net, October 2026.
Pi-hole is the project most people mean when they say “self-hosted DNS ad blocker,” and it has the largest community of anything in this guide, with 61.5K GitHub stars on its core repository. Since FTL v4.0 in 2018, the resolver engine (a fork of dnsmasq) has been compiled directly into FTL rather than running as a separate process, and Pi-hole v6 moved the web server and REST API into the same binary, dropping lighttpd and PHP. The project ships three coordinated version numbers per release: FTL (the resolver), Web (the dashboard), and Core (install/update scripts). The current set, released October 17, is Core v6.5, FTL v6.8 and Web v6.6.1.
Pi-hole uses the EUPL-1.2 license, an EU-originated copyleft license that’s uncommon in this space compared to the GPL, Apache, BSD and MPL licenses the rest of this list uses - worth knowing if your organization has a license-approval process. September and October were busy on the security side. FTL v6.7.1 (September 19) fixed two high-severity remote code execution bugs through the webserver.advancedOpts and misc.dnsmasq_lines settings, and those two options can no longer be changed from the API or web interface, only in pihole.toml, environment variables or pihole-FTL --config. The October release fixed another batch, including root privilege issues in Core and a bug that let read-only app sessions read password hashes and the TOTP secret. Its docs ask for just 512MB of RAM, so it runs on very small hardware, but “simple to set up” doesn’t mean “safe to leave unpatched.”
Key Features:
- Simplest, most widely documented ad-blocking DNS sinkhole to set up
- Huge community-maintained blocklist ecosystem
- Web dashboard plus a scriptable
piholeCLI - Optional built-in DHCP server with group/client management
License: EUPL-1.2 | Language: Shell (core) / C (FTL) | GitHub Stars: 61.5K+ (core), 1.7K+ (FTL) | GitHub
9. Blocky - Lightweight, YAML-Configured, Built for Observability

Screenshot: 0xerr0r.github.io/blocky, October 2026.
Blocky is a config-file-first alternative to AdGuard Home and Pi-hole aimed at people who want Prometheus/Grafana observability and Kubernetes-friendly deployment more than a heavyweight web UI. It’s entirely YAML-driven, stateless by default (no database required to run), and ships as a small multi-arch Docker image with a community Helm chart for cluster deployment.
Feature-wise, Blocky can use DoH, DoT and DoQ (RFC 9250) upstreams and can serve DoH itself, including over HTTP/3 (RFC 9114). It has per-client-group allow/deny lists with regex matching, deep CNAME inspection to catch cloaked tracker domains, conditional forwarding, upstreams per client group, and prefetching of often-used queries. It has kept a fast release pace: v0.34.0 (July 27) gave DNS rebinding protection its own response type in the stats, and v0.35.0 (September 5) added a per-client response metric, a “refused” block type and MIPS64 builds, plus a fix so DNSSEC records aren’t returned to clients that didn’t ask for them. Query logs can go to CSV, SQLite, MySQL/MariaDB, PostgreSQL or TimescaleDB for longer-term analysis.
Key Features:
- Per-client-group allow/deny lists with regex and deep CNAME inspection
- Conditional forwarding, per-client-group upstreams and prefetch caching
- Prometheus metrics with prebuilt Grafana dashboards
- Stateless operation - no database required just to run it
License: Apache-2.0 | Language: Go | GitHub Stars: 7K+ | GitHub
10. SmartDNS - Fastest-IP-Wins Resolution

Screenshot: pymumu.github.io/smartdns, October 2026.
SmartDNS solves a different problem than the ad-blocking tools above: instead of blocking domains, it queries multiple upstream resolvers in parallel for the same domain and returns whichever answer resolves to the fastest-responding IP address. It’s packaged for OpenWrt, including a LuCI app, and suits routers and homelabs where picking the lowest-latency CDN edge matters more than filtering.
SmartDNS supports DoT, DoH, DoQ, and DoH3 as upstream client protocols, DNS64 for IPv4-to-IPv6 gateway setups, per-client policy control by MAC or IP address, and a domain-suffix matching engine the project claims can evaluate 200,000+ rules in under a millisecond. An optional Rust-based web UI plugin (smartdns-ui, on port 6080 in the sample config) handles query monitoring. Release 48 (May 2026) added HTTP/2 support and DNS Discovery of Designated Resolvers (DDR, RFC 9462). The project has been quieter since: Release 48.3 (July 27) and 48.4 (August 5) were crash and bug fixes, and the last push to the GitHub repository was on August 30.
Key Features:
- DNS64 for IPv4-to-IPv6 gateway scenarios
- Per-client (MAC/IP) policy control
- Domain-suffix matching engine claimed to handle 200K+ rules in under 1ms
- Standalone web UI plugin for query monitoring and stats
License: GPL-3.0 | Language: C | GitHub Stars: 11.3K+ | GitHub
11. Unbound - The Default Validating Resolver on BSD and pfSense

Screenshot: nlnetlabs.nl/projects/unbound, October 2026.
Unbound from NLnet Labs is a validating, recursive, caching DNS resolver. It isn’t built to host your zones (NLnet Labs makes NSD for that), though its auth-zone feature can load a zone, such as a local copy of the root, and even answer for it. It ships in the base system of the major BSDs and is the default resolver behind pfSense and OPNsense, which makes it a common home-lab pick even though it does real recursion instead of forwarding. It validates DNSSEC once a root trust anchor is configured (the bundled unbound-anchor tool sets one up), supports DoT, DoH, and DoQ as a server, and can act as a DNSCrypt endpoint. Aggressive NSEC caching reduces the number of queries it needs to send upstream, and EDNS Client Subnet support lets it pass along approximate client location for CDN-friendly answers when needed.
Unbound moved to a new 1.26 line on August 4, which updated the root trust anchor certificates that unbound-anchor uses and tightened how the ipsecmod hook script is run. Then came two consolidated security releases: 1.26.1 (September 16) fixed nine CVEs, including a heap buffer overflow with possible remote code execution when digesting DNSKEY records, and 1.26.2 (October 21) fixed five more, including a cache-poisoning side channel exposed through unwanted-reply-threshold. For a validating resolver in front of a network, staying current matters more than feature-chasing.
Key Features:
- DNSSEC validation, with aggressive NSEC caching on by default
- Optional Redis-backed shared response cache for resolver clusters
- Extensive runtime statistics and a
cache_lookupcontrol command - Focused on resolving; authoritative hosting is left to its sibling NSD
License: BSD-3-Clause | Language: C | GitHub Stars: 5K+ | GitHub
Honorable Mentions
A few adjacent projects are worth knowing about even though they didn’t make the main list:
Knot Resolver - CZ.NIC’s recursive counterpart to Knot DNS, built around a modular, Lua-scriptable core with DNS-over-TLS and DNSSEC validation. Version 6.5.1 shipped on October 22, 2026. GPL-3.0-or-later. Worth pairing with Knot DNS if you want one vendor for both authoritative and recursive roles.
dnsdist - PowerDNS’s dedicated load-balancer and firewall component, useful for spreading query load across multiple backend resolvers or authoritative servers and filtering abusive traffic before it reaches them. The current release is 2.1.3 (October 12, 2026). GPL-2.0, C++.
dnsmasq - the small DNS forwarder and DHCP server inside OpenWrt and countless home routers, and the code Pi-hole’s FTL embeds. Version 2.93 came out in June 2026. It’s licensed under GPL version 2 or 3, at your choice. Pick it when you want a lightweight cache and DHCP server with no web UI.
Stubby (getdns) - a stub resolver that forwards local queries to an upstream DoT resolver, for encrypted DNS on one machine. Its last release, v0.4.3, dates from December 2022.
How to Choose the Right DNS Server
If you’re hosting zones for a domain you own - your own website, a small business, a registrar-style operation - PowerDNS is the most practical starting point because of its database backends and REST API; reach for Knot DNS or NSD if raw authoritative throughput and a minimal attack surface matter more than ease of integration. If you need a validating recursive resolver in front of a network, Unbound is lean and focused, while BIND is the safer choice if you also need authoritative zones on the same box and don’t mind its larger footprint and its monthly patch cadence. If you’re running Kubernetes, you already have CoreDNS - the only decision is which plugins to enable.
For a home network or small office where the goal is “block ads everywhere and stop leaking my browsing history to my ISP,” Pi-hole remains the easiest on-ramp thanks to its documentation and community blocklists, AdGuard Home is the better choice if you want a more modern web UI and native encrypted-DNS support, and Blocky fits best if you’re already running Prometheus/Grafana and want your DNS metrics alongside everything else. If you want one server that does real recursion and authoritative hosting and DHCP with a full-featured web console, Technitium DNS Server is the most capable single option in this guide.
Whichever you choose, “watch releases and patch within a week” is a reasonable default for anything that answers queries from untrusted networks.
For related infrastructure decisions, see our guides on WireGuard vs OpenVPN for self-hosting and fixing DNS_PROBE_FINISHED_NXDOMAIN if you run into resolution errors while switching resolvers.
Remotely Manage Your Self-Hosted DNS Server With Pinggy
Once your DNS server is running, you’ll likely want to check its dashboard or adjust a blocklist without being on the same network - from your phone, from work, or while traveling. Pinggy can expose that admin web UI over HTTPS with a single SSH command, without opening a port on your router.
For example, AdGuard Home serves its first-run setup wizard on port 3000 and its dashboard on port 80 by default. With the dashboard on port 80:
ssh -p 443 -R0:localhost:80 -t free.pinggy.io b:admin:change-meThe b:admin:change-me keyword adds HTTP basic auth in front of the tunnel, which matters here since you’re exposing an administrative interface; pick your own username and password, neither of which can contain a colon. The same command works for Technitium’s console on port 5380 or Pi-hole’s dashboard on port 80, by changing the local port. Free tunnels run for 60 minutes; for a link that stays up, use a Pinggy Pro token with a persistent subdomain.
One important caution: this pattern is for the web UI, not the raw DNS port. Publicly exposing port 53 itself turns your resolver into an open DNS server that anyone on the internet can query - and if it performs recursion, that’s a well-known vector for DNS amplification abuse. Keep port 53 reachable only from networks you trust, and use a tunnel like this only for the management interface, with authentication enabled.
Conclusion
There’s no single “best” open source DNS server - it depends on whether you need real infrastructure (PowerDNS, BIND, NSD, Knot DNS, CoreDNS, Technitium) or a home-network resolver or ad blocker (Unbound, Pi-hole, AdGuard Home, Blocky, SmartDNS). The harder part in 2026 is the maintenance load: with AI-assisted bug hunting driving a wave of CVEs, monthly security releases are now normal for the biggest projects. Whichever you pick, keep it patched, restrict who can query it, and verify it’s resolving correctly with dig before switching your network over.